Create Custom Action
1. Navigate to Custom Actions List
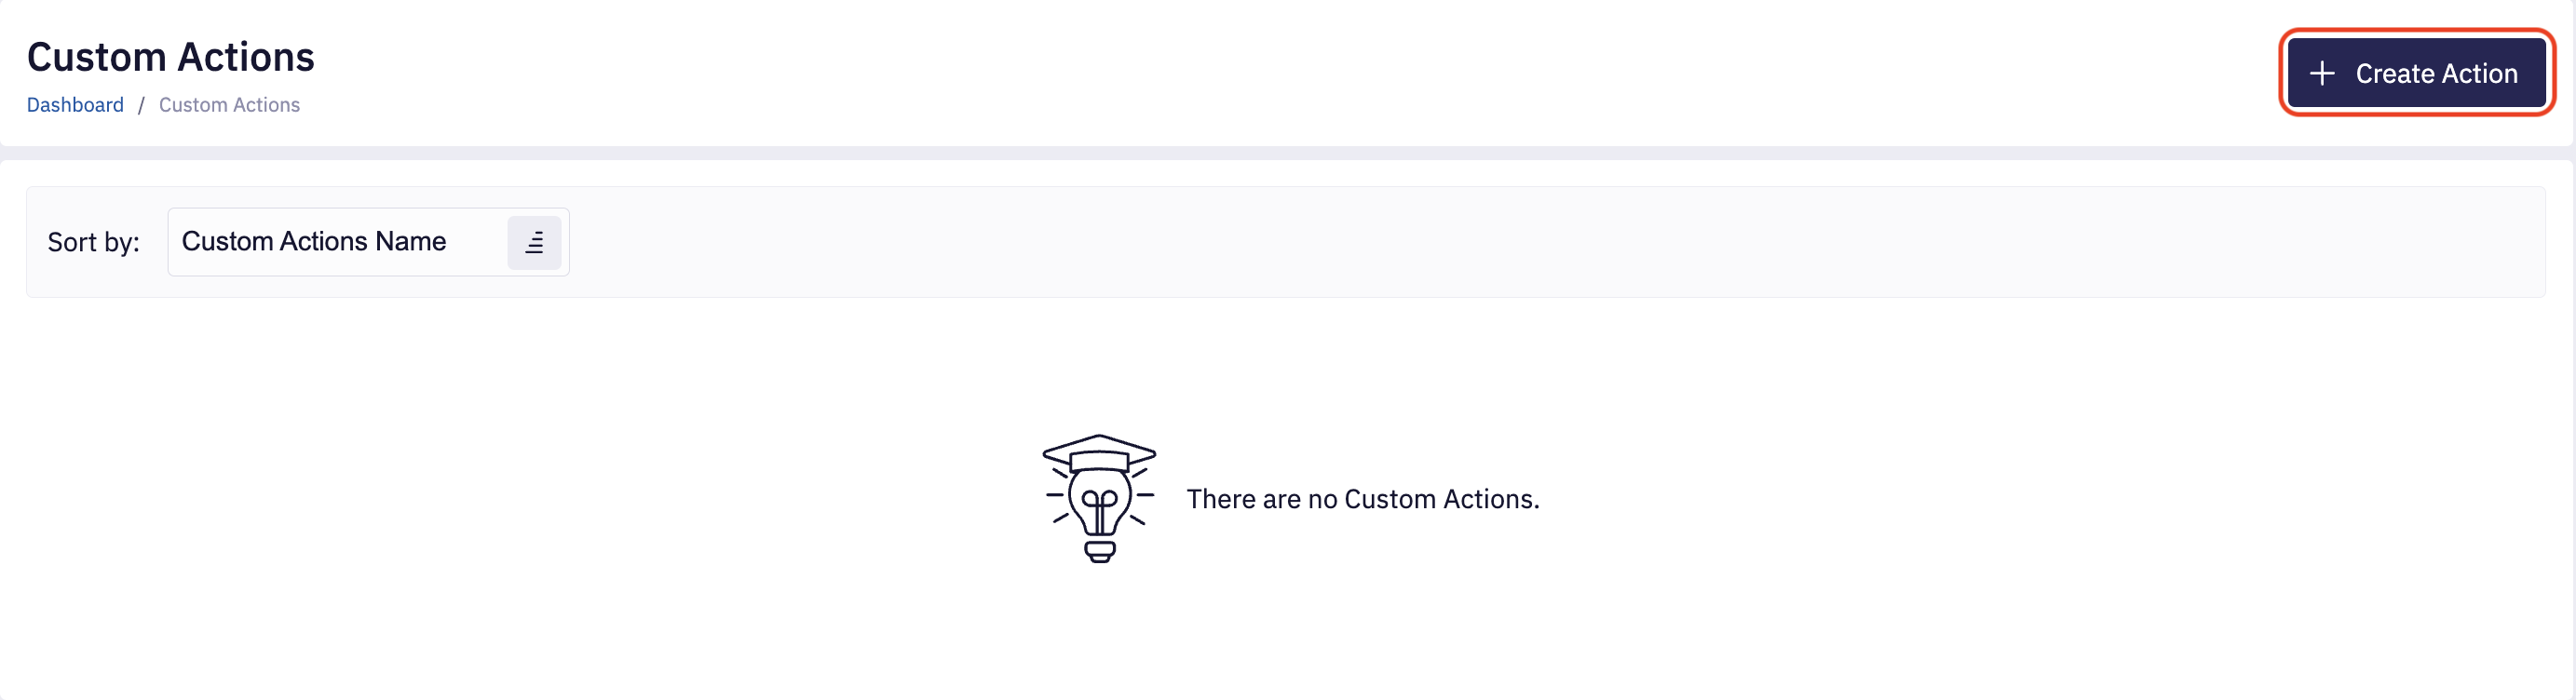
To create a Custom Action, select Custom Actions on the left menu. Then, click the Create Action button.
2. Fill in Action Details
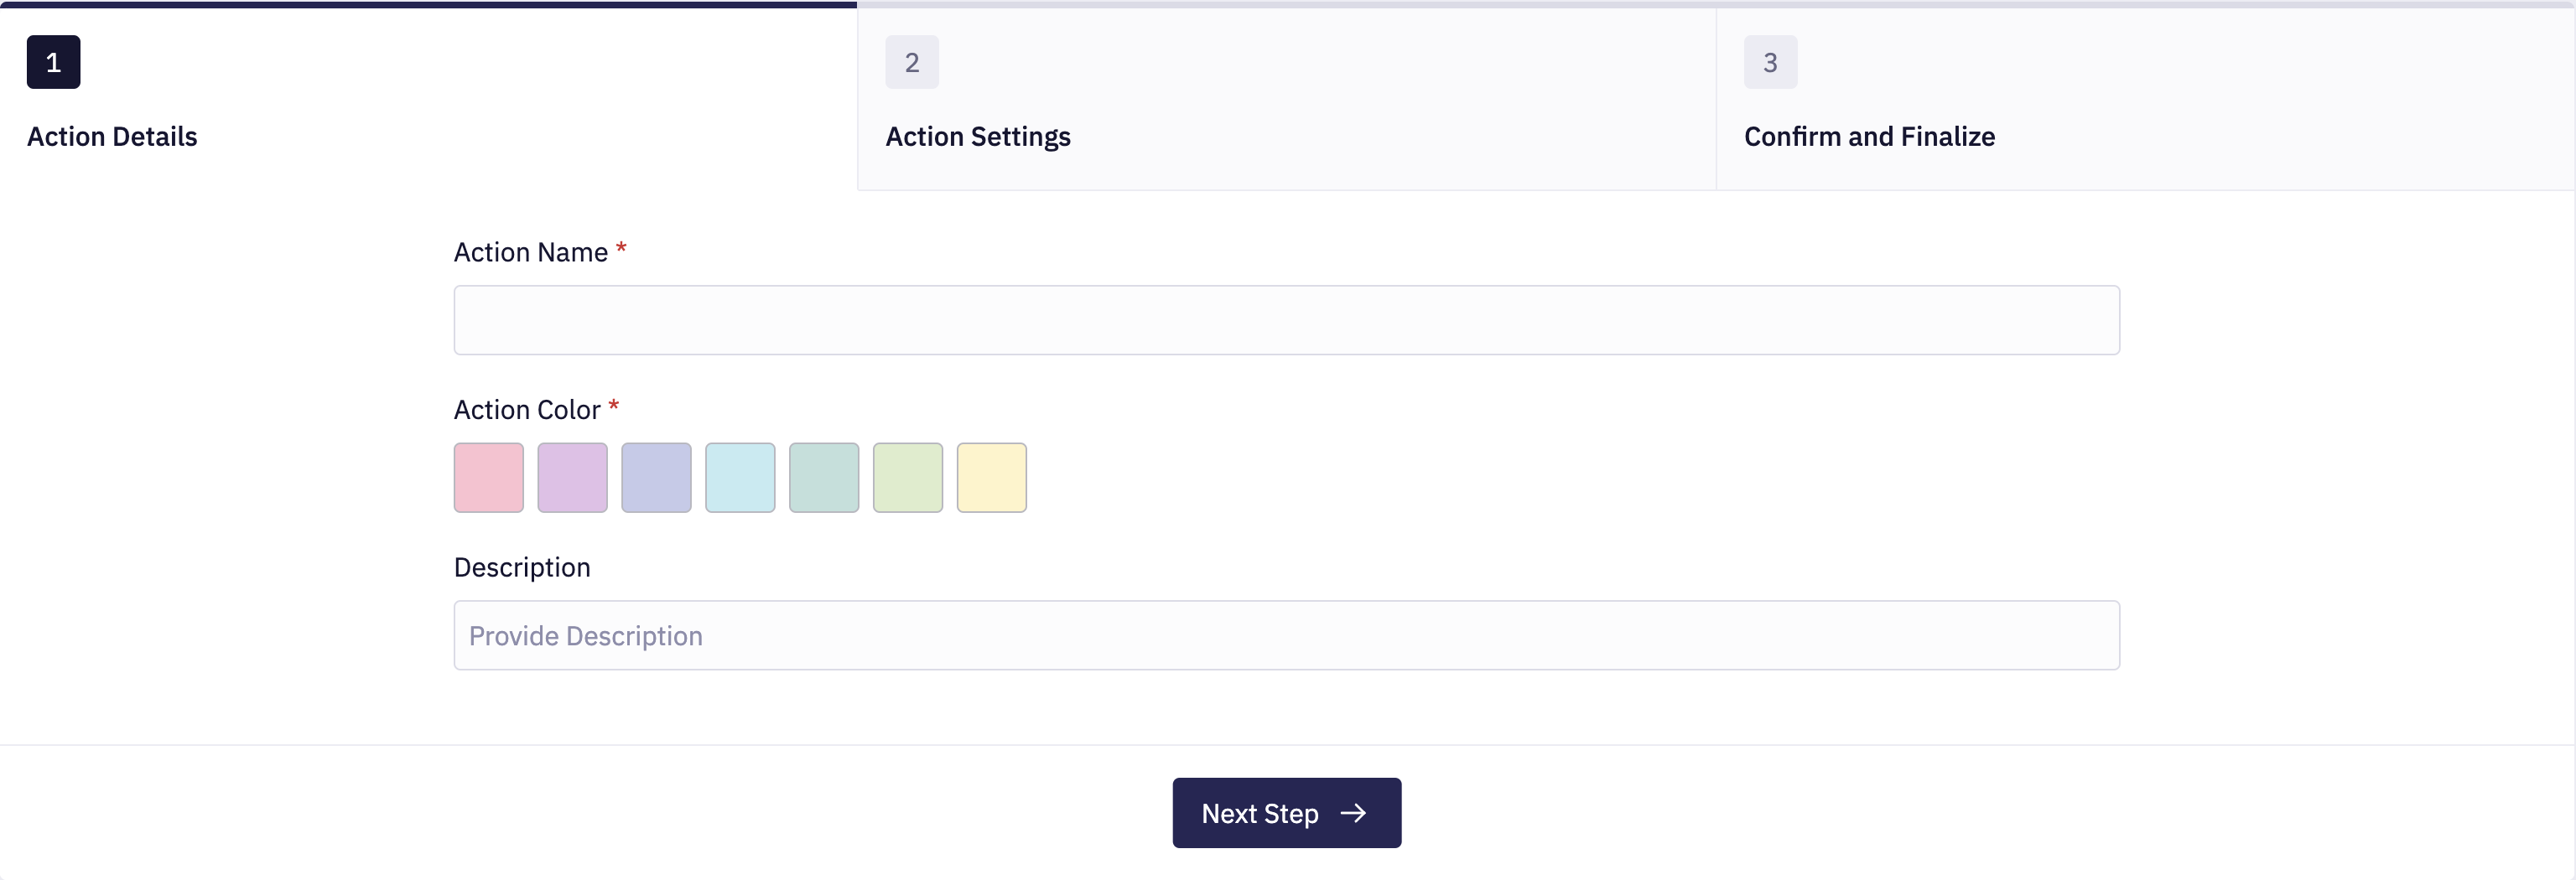
In this step, enter required Action Name and select an Action Color. Providing description is optional.
3. Define Action Settings
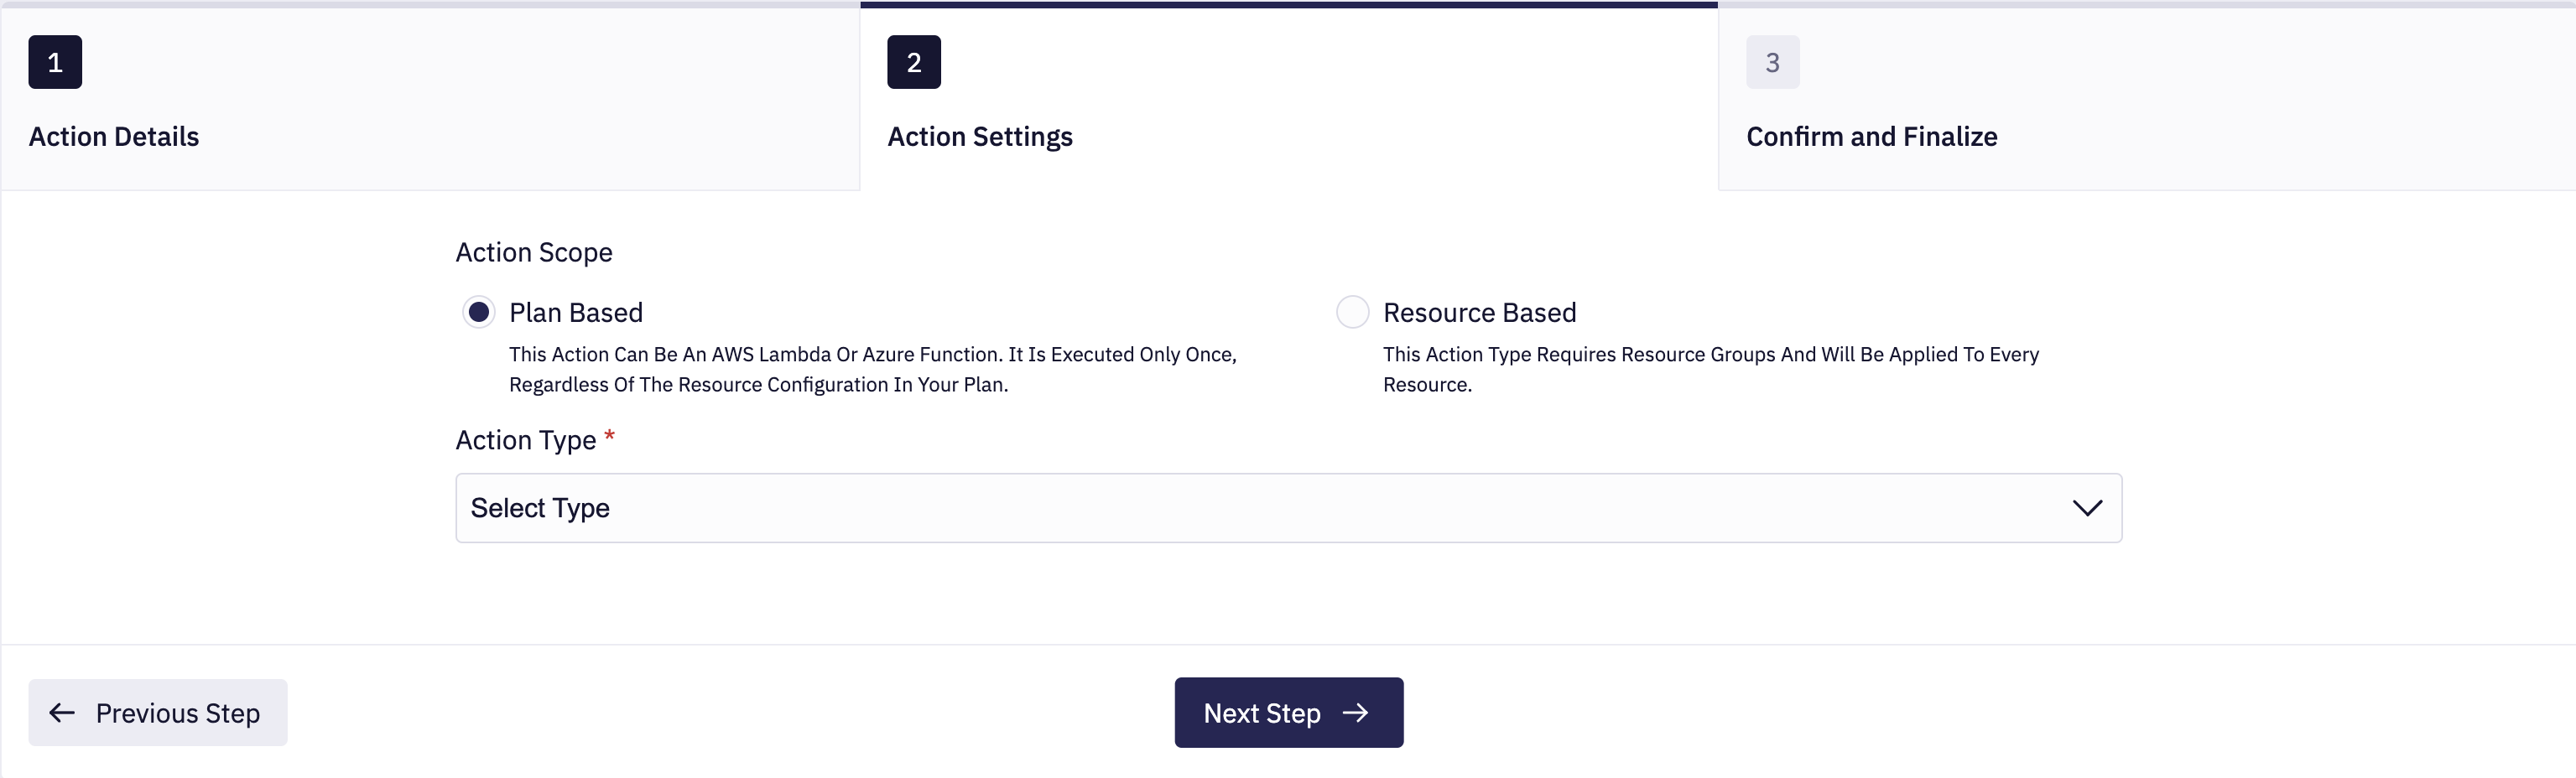
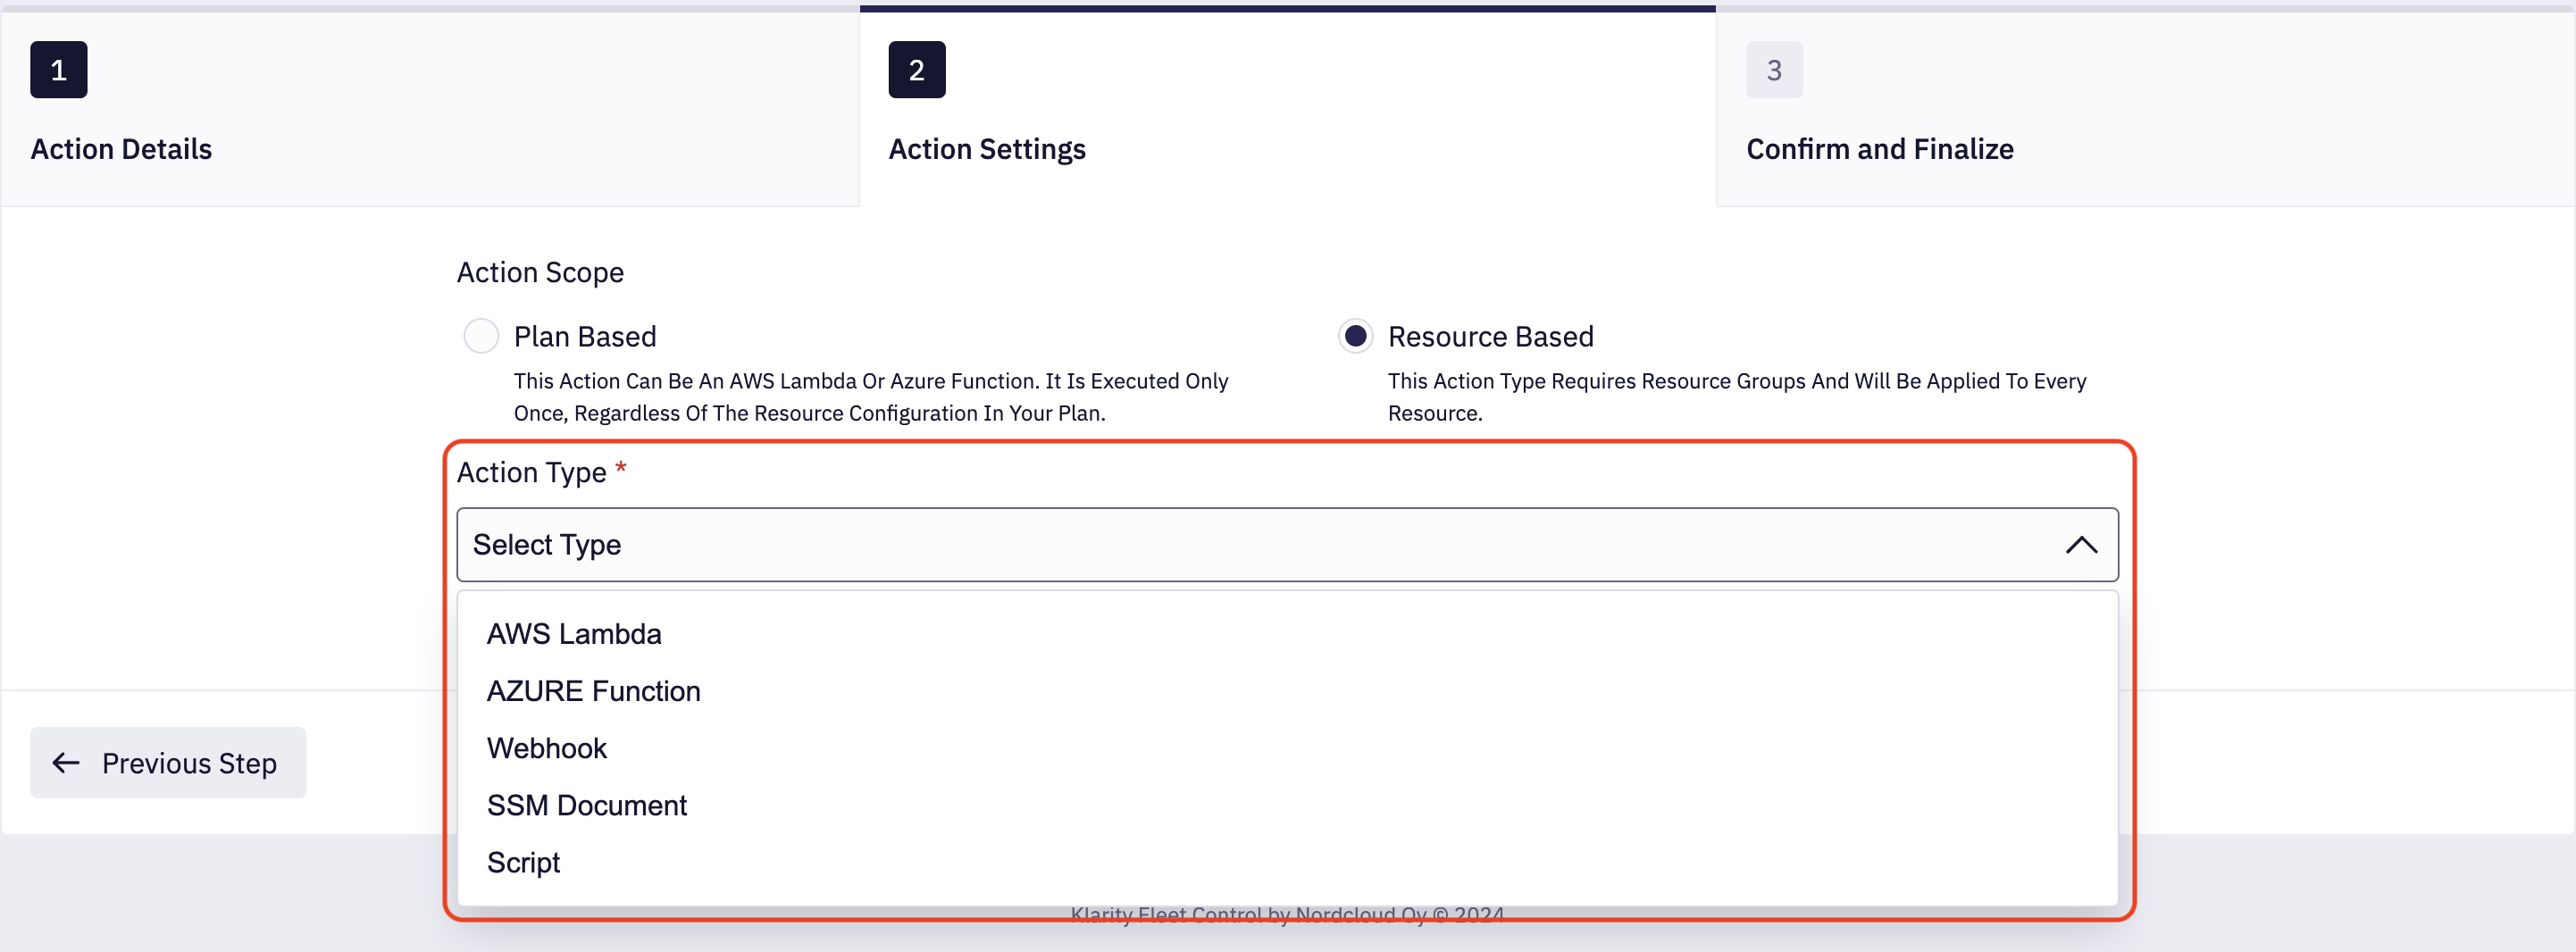
In this step, you should choose Action Scope.
We have the following scopes:
- Plan-based: Action will be executed a single time in your plan.
- Resource-based: Action will be executed for every resource (based on Resource Groups).
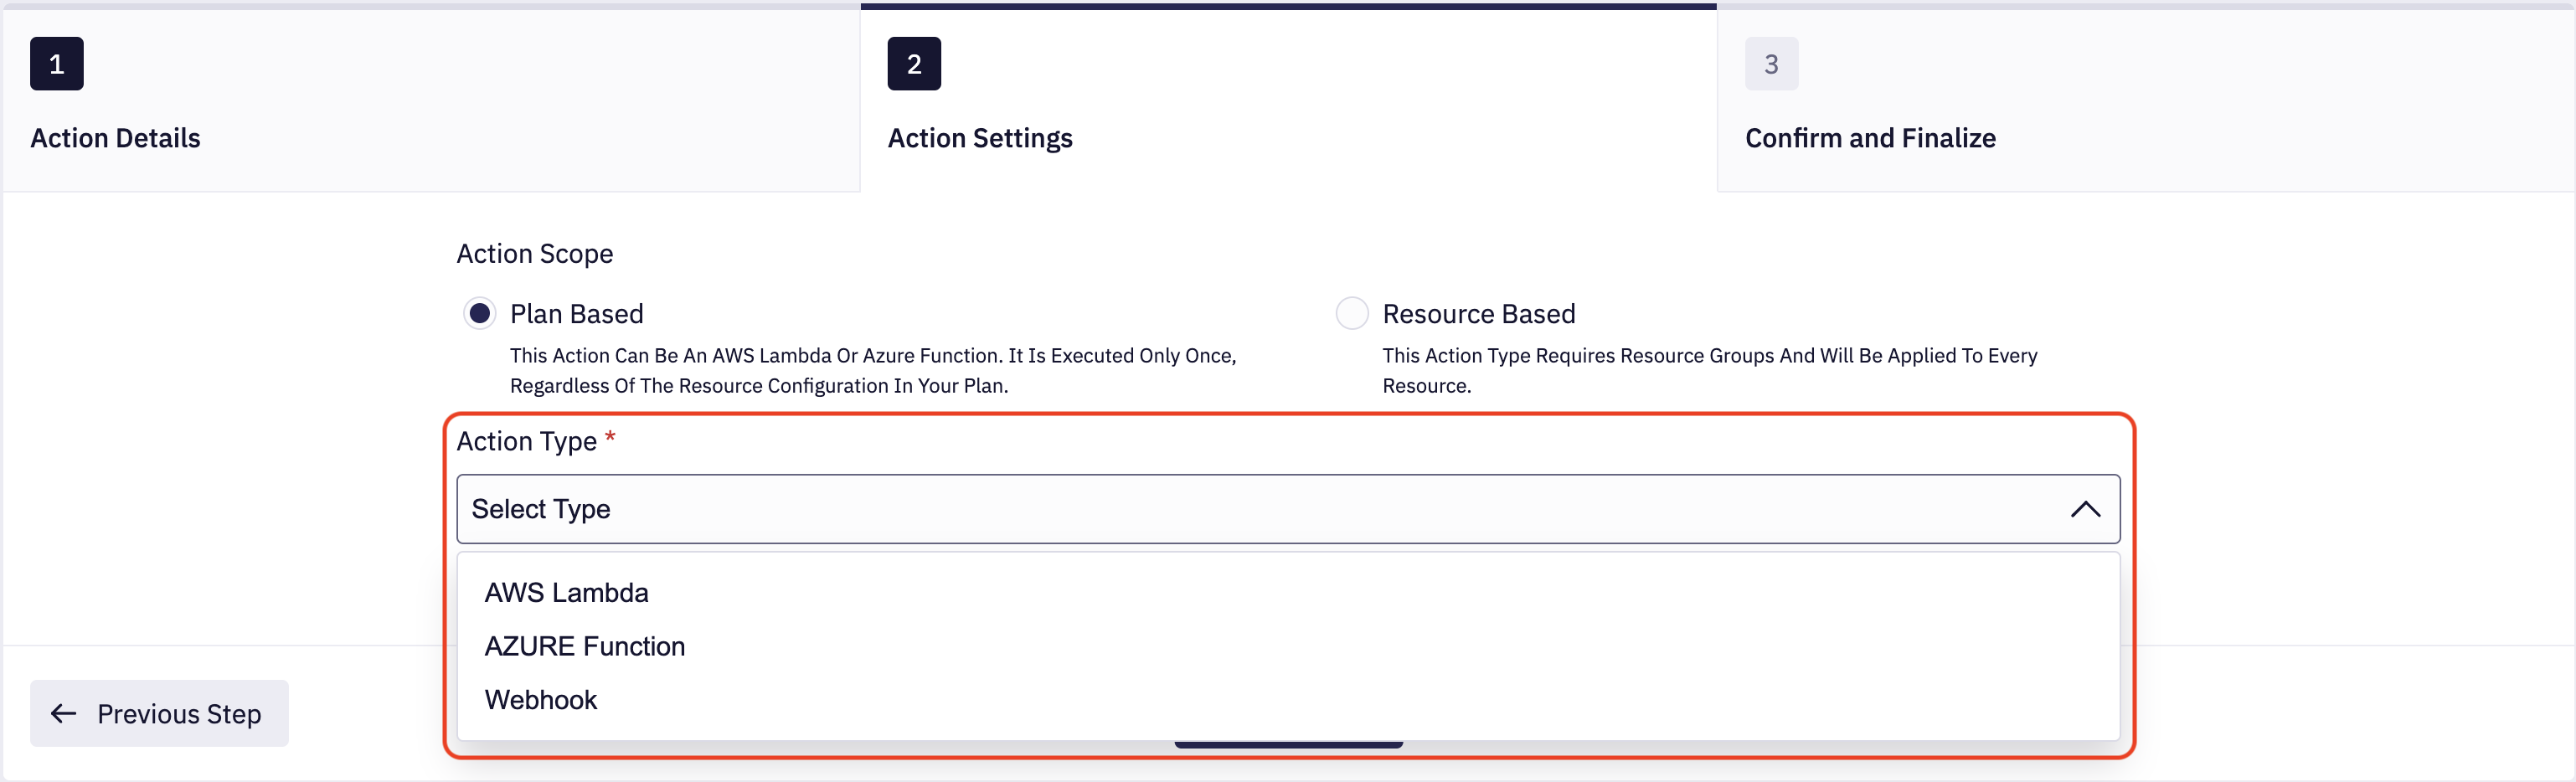
Next, you should select an Action Type and fill up required parameters.
For Plan-based scope, user can define one of these types:
- AWS Lambda: Executes a Lambda function using the provided ARN. Lambda must have a resource-based permission policy configured allowing Fleet Control to invoke it. The Configuring AWS Lambda Permissions section below explains how to configure these permissions.
- AZURE Function: Executes a function using provided function URL, HTTP Method and Access Key ID.
- Webhook: Executes a webhook using provided URL, HTTP Method, Payload and HTTP Headers.
For Resource-based scope, user can use one of these types:
- AWS Lambda: Executes a Lambda function using the provided ARN. Lambda must have a resource-based permission policy configured allowing Fleet Control to invoke it. The Configuring AWS Lambda Permissions section below explains how to configure these permissions.
- AZURE Function: Executes a function using provided function URL, HTTP Method and Access Key ID.
- Webhook: Executes a webhook using provided URL, HTTP Method, Payload and HTTP Headers.
- SSM Document: Triggers an AWS SSM Document using its SSM Document Identifier.
- Script: Executes a custom script provided during action creation.
For Resource-based Script, ensure that your script exits with the proper exit status. Without this, the event action status for the resource won't be reported accurately.
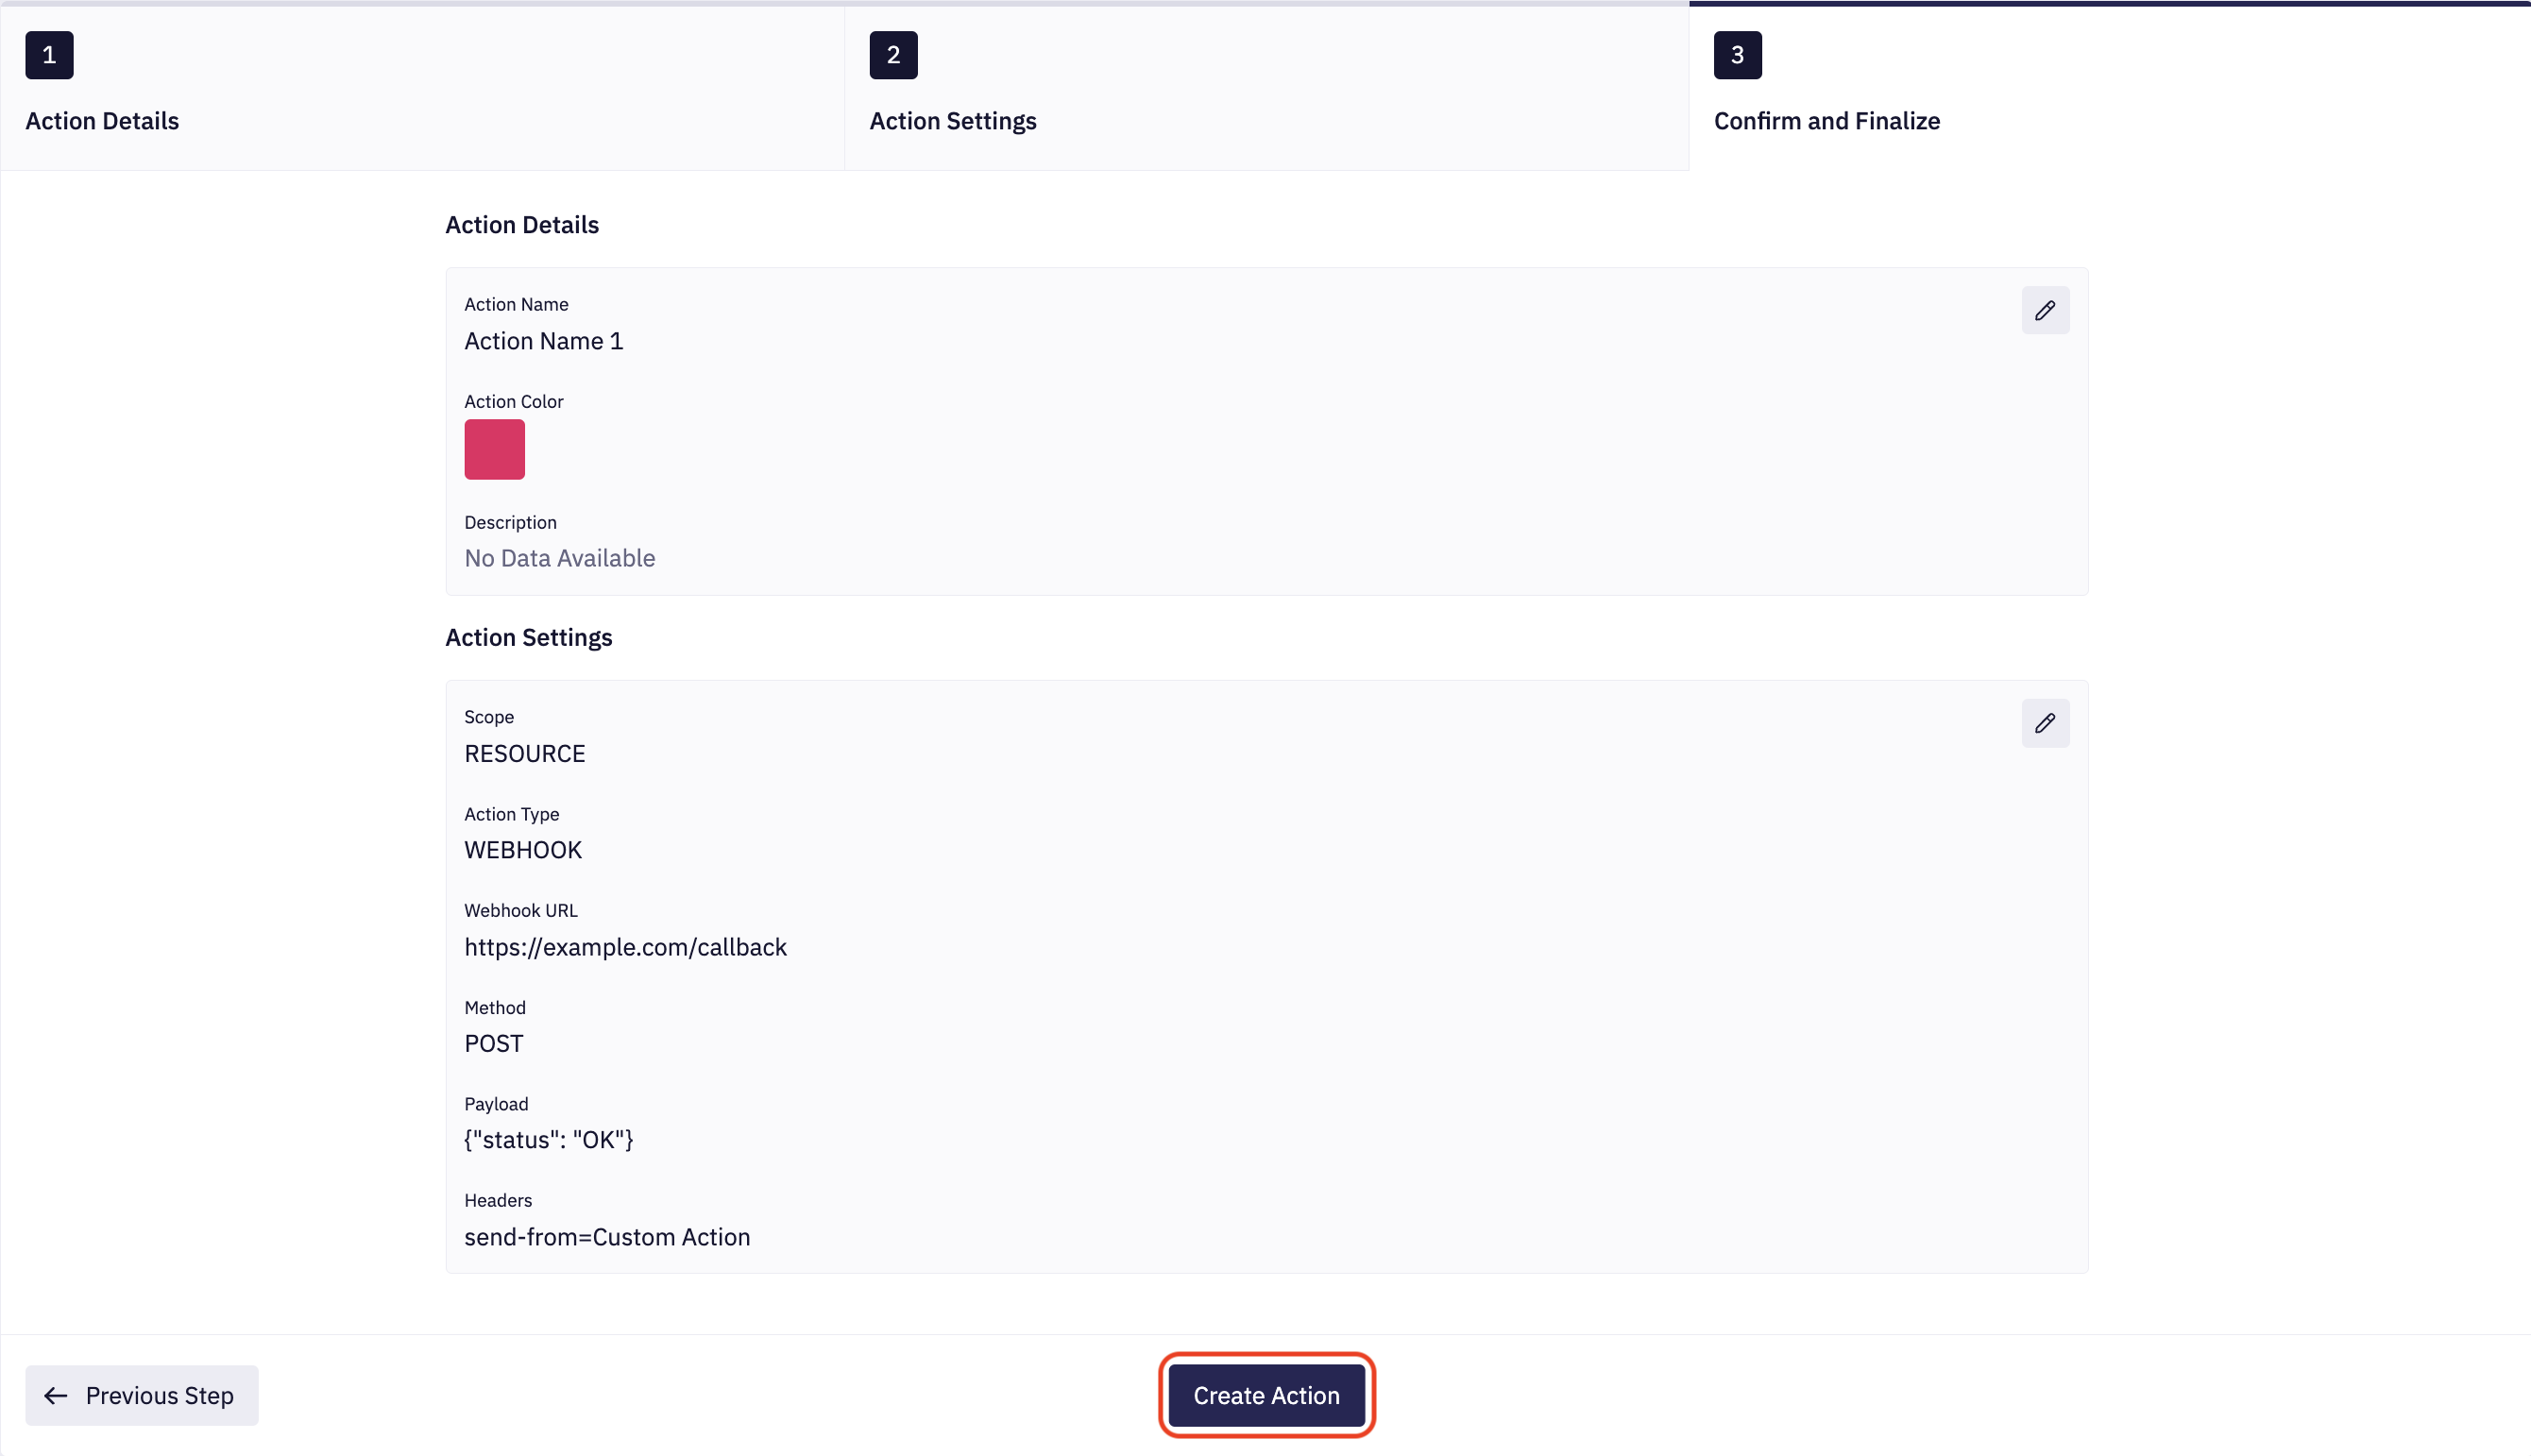
4. Confirm and Finalize
In the last step, make sure that provided data is correct and click Create Action button.
Configuring AWS Lambda Permissions
For the Fleet Control to invoke your AWS Lambda function, the Lambda function needs to have a resource-based permission policy configured. Refer to the AWS documentation for a detailed step by step guide and various configuration options.
Here is an example AWS CLI command you can use to add the required permission policy to your Lambda function:
aws lambda add-permission --function-name '<LAMBDA NAME>' --statement-id '<STATEMENT NAME>' --action 'lambda:InvokeFunction' --principal '286863837419'
Substitute <LAMBDA NAME> with the name of your Lambda function and <STATEMENT NAME> with a unique name
for the statement.
286863837419 is the Fleet Control AWS account ID.